


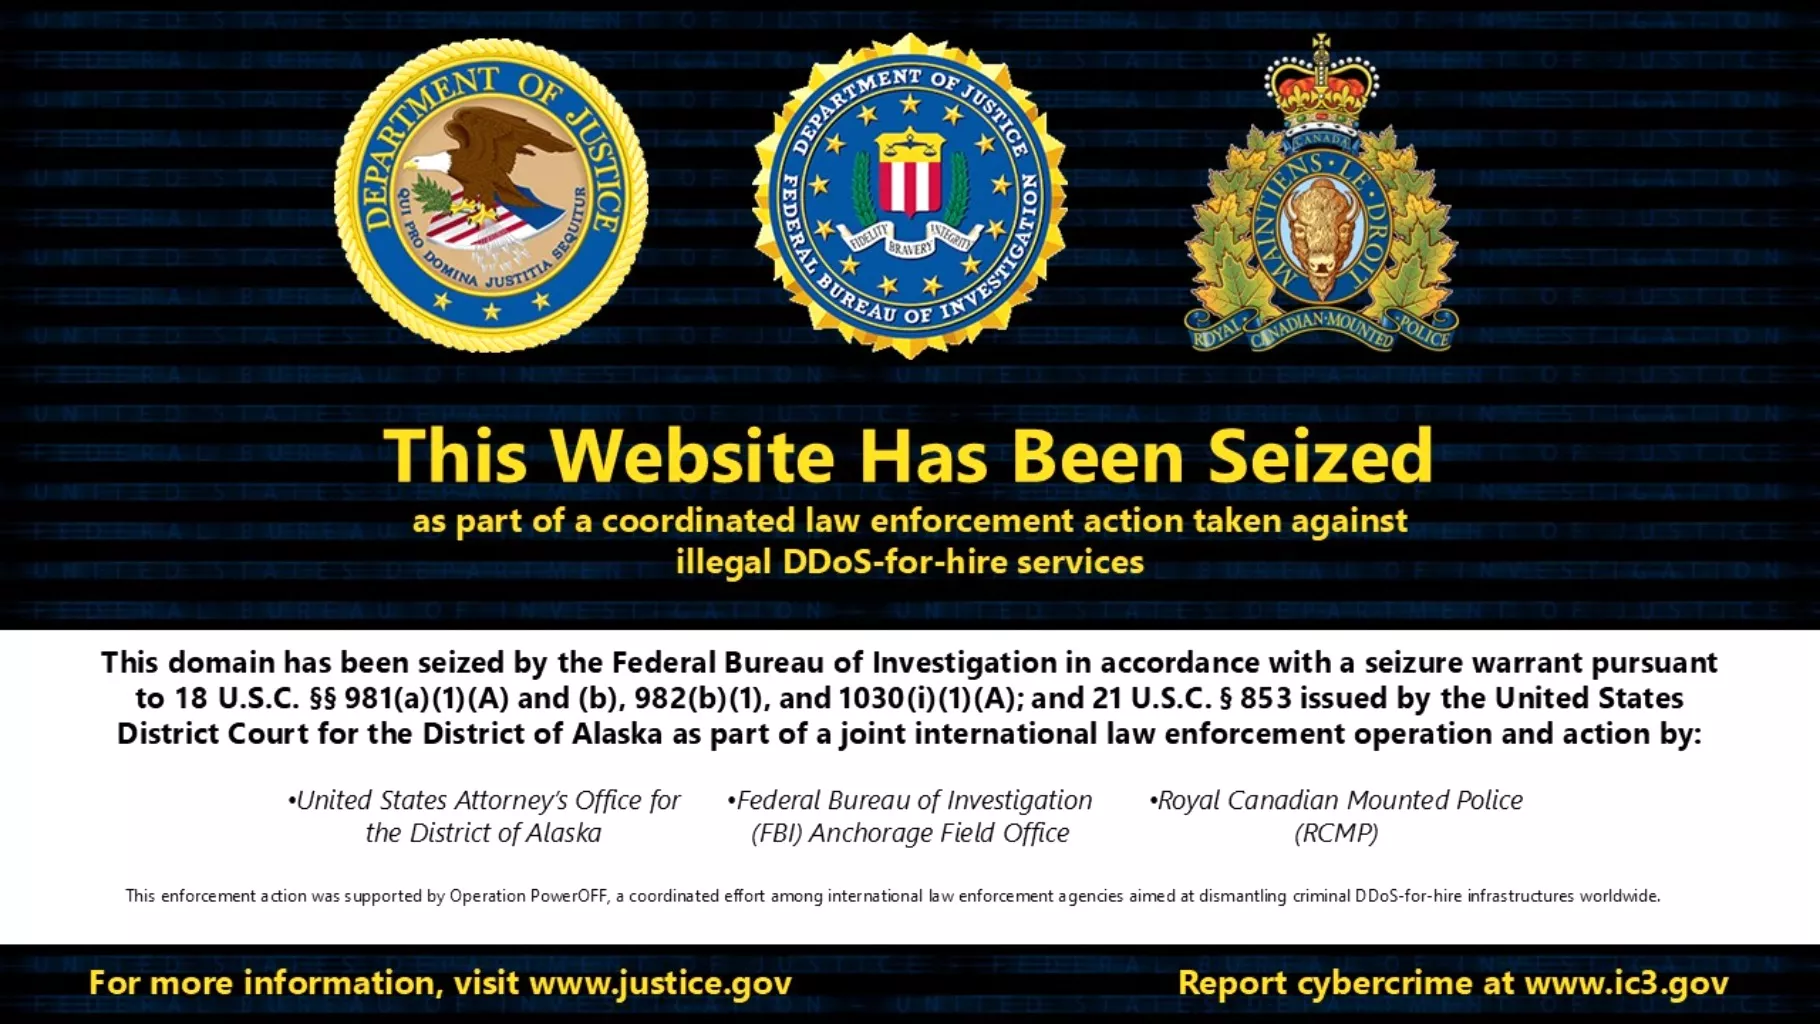
The FBI seized two domains of NightmareStresser, a paid DDoS attack service. According to U.S. authorities, NightmareStresser was one of the oldest active DDoS services, and since 2022 it has been used for hundreds of thousands of attacks worldwide. Law enforcement confiscated the domains nightmare-stresser[.]com and nightmarestresser[.]org, and now they display a “FBI block page” informing of the seizure as part of an international operation involving U.S. law enforcement and the Royal Canadian Mounted Police.
NightmareStresser belonged to the category of so‑called “booter” and “stresser” services, which are on‑demand DDoS attack solutions. While a booter is a service that allows malicious actors to order a DDoS attack against any website or Internet‑connected device, a stresser provides the same functionality but is theoretically intended for legitimate testing of web resource reliability and the underlying infrastructure.

According to the report by Searchlight Cyber experts in 2023, NightmareStresser had more than 566,000 registered users, and its infrastructure included 52 dedicated servers. The platform allowed attacks on L4 and L7 targets, and the DDoS attack power could reach 200 Gbit/s.
On its own website, the operators advertised NightmareStresser as “the only DDoS tool available 24/7” and claimed that the service had been running continuously for over eight years. Platform customers could select the target’s IP address or URL, the port, and the number of simultaneous attacks, and among the service’s available features were CAPTCHA bypass, geoblocks, and request‑rate limits. NightmareStresser operators accepted cryptocurrency payments.
U.S. Department of Justice representatives state that such DDoS services are used to attack educational institutions, government organizations, gaming platforms, and other targets. Moreover, the attacks not only take specific resources offline but can also significantly degrade Internet service performance for many users.
The seizure of NightmareStresser’s domains occurred as part of the international operation PowerOFF, ongoing since 2018 and targeting on‑demand DDoS attack services. In previous years, law enforcement agencies in various countries have shut down more than one hundred DDoS‑related domains and have brought charges against 12 individuals. For example, in April 2026 alone, as part of a new phase of the operation, 53 domains were taken down and four people were arrested.
It should be noted that NightmareStresser had previously been targeted by law enforcement. For instance, in December 2022 U.S. authorities seized nightmarestresser[.]com as part of the confiscation of 48 domains linked to various DDoS services.
