The ShinyHunters group has hacked the Onion site of the ransomware group Clop (also known as Cl0p). ShinyHunters members claim to have stolen data from the server, including logs, source code and private keys of the onion service, and now intend to demand a ransom from the kidnappers.
According to BleepingComputer, the attack occurred on the evening of Friday, September 18, 2026. ShinyHunters representatives told journalists they had found a vulnerability in the CMS that allows unauthenticated file uploads and initially uploaded a small text file to Clop’s server. In it, the hackers wrote “pwn3d by ShinyHunters”, advised Clop not to threaten them again and left a link to their site. Journalists confirmed that this file was indeed present on Clop’s server and was being downloaded directly from the group’s Tor site.
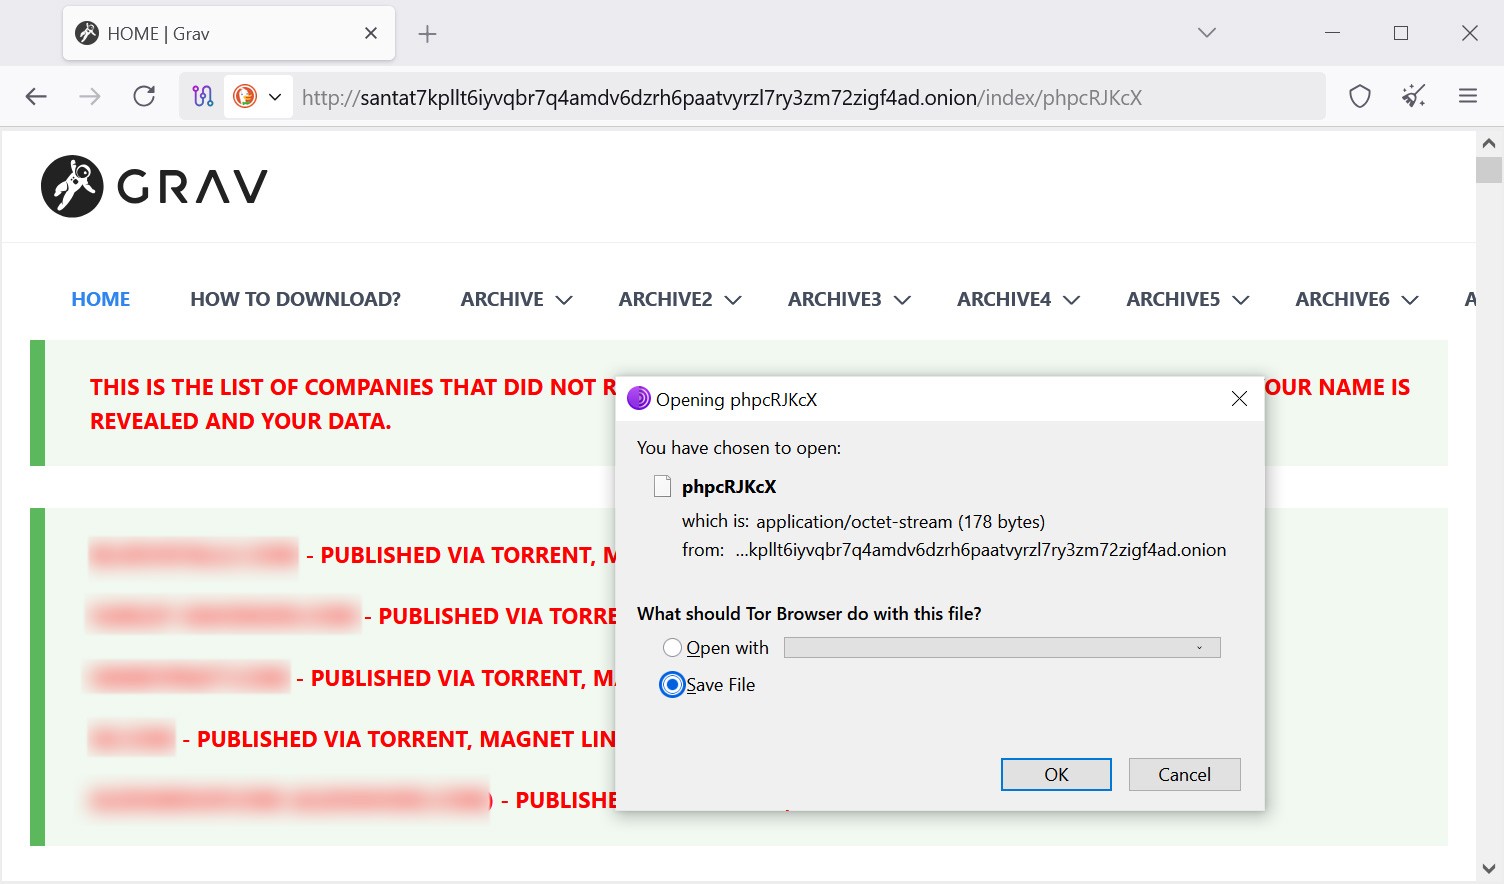

A few hours later, ShinyHunters completely replaced the site’s content: an ASCII image of the Pokémon Umbreon (Umbreon), which the group uses as its logo, a link to the ShinyHunters site and a message “rooting your systems since ’19 ;)”. It is noted that the same image was used during the deface of HackForums in August 2020, for which ShinyHunters members also claimed responsibility.
Group representatives said they obtained “full access” to Clop’s server, having stolen the source code, the Grav CMS plugins and other files. Additionally, the attackers allegedly extracted the contents of /var/log, where system and authentication logs could be found, including the IP addresses of users who connected to the server.
ShinyHunters also claims to have stolen the private keys of Clop’s onion service, which means the attackers can launch their own Tor server with the same onion address even after Clop regains control of its infrastructure.
Now ShinyHunters are reviewing the obtained data and state that they are extorting Clop and plan to soon publish the ransom demand on their site.
The hackers explain that what happened is revenge for a recent conflict that arose between the groups. According to ShinyHunters’ version, the hacker feud began during Clop’s campaign targeting Oracle E-Business Suite in 2025. We recall that at that time the kidnappers exploited several vulnerabilities, including the 0‑day vulnerability CVE-2025-61882, and massively stole corporate data.
Around that time, members of the hacker group Scattered Lapsus$ Hunters (which includes ShinyHunters) published a public‑domain PoC exploit. As later confirmed by Oracle, this PoC matched the exploit used in Clop’s attacks. At the time, ShinyHunters claimed that initially the exploit belonged to them and that a Clop member had obtained and used it without permission.
BleepingComputer writes that after this the conflict between cybercriminals escalated: according to ShinyHunters, a Clop representative threatened to reveal the identities of the group’s members and to take physical revenge against them.