


 News
 Discover
 Newsletter
Latest news
 Cybercrime
The Virginia Department of Elections database may have been hacked and is online on the dark web
A serious security incident appears to have hit the Virginia Department of Elections, causing the unauthorised dissemination of a large...
Pietro Melillo - June 30, 2024
 Cybercrime
Identified a POC for the CVE-2024-34102 Vulnerability in Magento / Adobe Commerce
Recently, a Proof of Concept (POC) for a vulnerability identified as CVE-2024-34102, which affects the Magento and Adobe Commerce e-commerce...
RHC Dark Lab - June 29, 2024
 Cybercrime
Cyberpunk 2077: Source Code Stolen?
A malicious actor has claimed to have obtained access to the complete source code of Cyberpunk 2077, the famous role-playing...
Pietro Melillo - June 29, 2024
 Cybercrime
Alleged Leak of the 2020 Israeli Voter Database
In a significant and concerning development, an individual using the alias "mrwan" has allegedly leaked the 2020 Israeli voter database....
RHC Dark Lab - June 28, 2024
 Cybercrime
TeamViewer: Irregularity Detected in Internal IT Environment
TeamViewer, a leading company in the remote access and support software sector, has announced that it has detected an irregularity...
RHC Dark Lab - June 28, 2024
 Cybercrime
RansomHub criminal hackers claim cyber attack on Coca Cola
Today, the RansomHub gang of cybercriminals claimed on their Data Leak Site (DLS) an IT attack on Coca Cola. We...
RHC Dark Lab - June 27, 2024
 Cybercrime
Threat Actor “DragonForce” Seeks New Partners
A recent post on a dark web forum reveals that a cybercriminal group known as "DragonForce" is actively seeking new...
RHC Dark Lab - June 27, 2024
 Cybercrime
Cyber catastrophe in sight? The new Bug on MOVEit has an Online PoC Exploit
In the realm of cybersecurity, vulnerabilities constantly represent a significant risk for businesses and institutions. Many system administrators may recall...
RHC Dark Lab - June 27, 2024
 Cybercrime
UNZIPPED DATA – LEVI STRAUSS COMPROMISED ACCOUNTS
The legendary Jeans retailer Levi Strauss & Co. identified a significant data breach that affected over 72,000 customers. The incident...
RHC Dark Lab - June 26, 2024
 Cybercrime
LockBit: The Bluff of Double Extortion Against the Federal Reserve
In recent years, the cybersecurity landscape has been dominated by the growing threat posed by ransomware groups. Among these, LockBit...
RHC Dark Lab - June 26, 2024
 Cybercrime
Xehook Stealer: The Rise and Sale of a Formidable Stealer Malware
Introduction Xehook Stealer is a sophisticated malware targeting Windows operating systems, first discovered in January 2024. Within a year, Xehook...
Pietro Melillo - June 26, 2024
 Cybercrime
WordPress: Five Plugins Found with Malicious Code
On June 24, 2024, Wordfence revealed a supply chain attack on WordPress plugins, leading to the compromise of five plugins...
Pietro Melillo - June 25, 2024
RHC interviews Ransomcortex, the gang targeting Hospitals. “pay the ransom, we won’t even spare the CEO’s family.”
Ransomcortex is a new cyber ransomware gang that resonates menacingly in the healthcare sector. This group has quickly attracted attention for its specialization in attacks on healthcare facilities, striking four...


Threat Actors IntelBroker Release Alleged Equifax Data on Underground Forum
Recently, a threat actor in an underground forum published an alleged data breach. This incident was revealed by a user named IntelBroker on BreachForums, a notorious online community for cybercriminal...
Hospitals tremble! Ransomcortex arrives. ransomware gang targeting healthcare facilities
Recently, the landscape of cyber threats has been enriched by the emergence of a new ransomware group named "Ransomcortex". This group is distinguished by its specialization in attacking healthcare facilities,...

RHC interviews Vanir Group. Former affiliates of LockBit, Karakurt and Knight united to extort money: ‘Hire professionals, don’t be cheap’
New threat actors often emerge every day to destabilize the digital foundations of organizations around the world. One of the most recent and disturbing cybergangs uncovered by Darklab of Red...

Alleged Data Breach of the United States Department of Defense and National Security Agency
Recently, alarming news has emerged on a well-known underground forum regarding alleged data breaches of the United States Department of Defense and the National Security Agency (NSA). The announcements, posted...
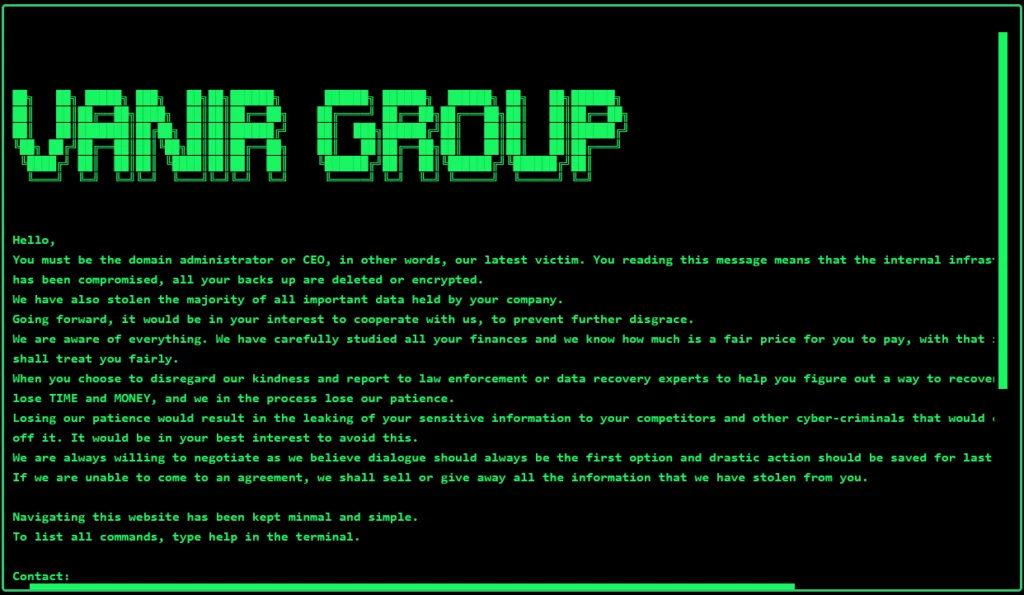
New Ransomware Group “Vanir Group”: Three Victims Immediately in Their Data Leak Site
A new ransomware group, calling themselves "Vanir Group," has recently made its debut in the cybercrime landscape. This group has quickly garnered attention for the aggressiveness and professionalism of their...

The Threat Actor 888 claims responsibility for a breach at Nokia.
A malicious actor, known by the alias "888," recently claimed responsibility for disclosing sensitive data belonging to Nokia. The attack, which occurred in July 2024, compromised a wide range of...

Alleged NATO Data BreachAlleged NATO Data Breach: 643 CSV Files with User Data and Server Details Leaked
A threat actor claims to have leaked sensitive data from NATO - TIDE (Think-Tank for Information Decision and Execution Superiority). NATO-TIDE (Think-Tank for Information Decision and Execution Superiority) is a...
Access to UK Accounting System for Sale: 600 Clients and 1TB of Data at Risk
A malicious actor is allegedly selling access to an RDWeb system in the United Kingdom, belonging to an accounting firm. This breach represents a serious threat to the security of...

China: 7.5 Million Tourist Data Stolen!
On the morning of July 6, 2024, a user known as "BlackKing" revealed a significant data breach involving a Chinese travel and tourism platform on a hacking forum. This information...